防火墻后面的 tinc
示例:防火墻后面的 tinc
當(dāng)在防火墻后面(而不是在防火墻本身上)運(yùn)行 tinc 時(shí),必須小心配置防火墻,以便允許 tinc
流量通過。此示例中包含示例防火墻規(guī)則。它們是為 iptables(Linux 2.4
防火墻代碼)編寫的,但已注釋,以便您可以將相同類型的規(guī)則應(yīng)用于其他防火墻。
示例:防火墻后面的 tinc
概述
運(yùn)行 tinc 的主機(jī)的配置
tinc 的配置
防火墻配置
概述
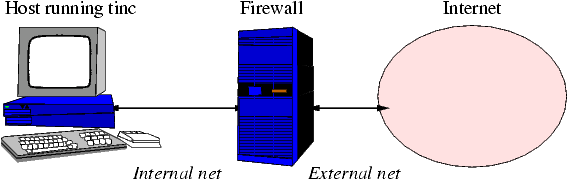
網(wǎng)絡(luò)設(shè)置如下:
內(nèi)部網(wǎng)絡(luò)為 123.234.123.0/24
防火墻 IP 為 123.234.123.1
運(yùn)行 tinc 的主機(jī)有 IP 123.234.123.42
主機(jī)想要連接的 VPN 的地址范圍為 192.168.0.0/16
主機(jī)有自己的 VPN IP 192.168.10.20
請(qǐng)注意,內(nèi)部網(wǎng)絡(luò)具有真實(shí)的 Internet 地址,因此完全可以從外部訪問(防火墻設(shè)置的限制除外)。如果內(nèi)部網(wǎng)絡(luò)具有私有地址,請(qǐng)參考偽裝防火墻示例。
運(yùn)行 tinc 的主機(jī)的配置
host# ifconfig
eth0 Link encap:Ethernet HWaddr 00:20:30:40:50:60
inet addr:123.234.123.42 Bcast:123.234.123.255 Mask:255.255.255.0
UP BROADCAST RUNNING MTU:1500 Metric:1
...
lo Link encap:Local Loopback
inet addr:127.0.0.1 Mask:255.0.0.0
UP LOOPBACK RUNNING MTU:3856 Metric:1
...
vpn Link encap:Point-to-Point Protocol
inet addr:192.168.10.20 P-t-P:192.168.10.20 Mask:255.255.0.0
UP POINTOPOINT RUNNING NOARP MULTICAST MTU:1500 Metric:1
...
host# route
Kernel IP routing table
Destination Gateway Genmask Flags Metric Ref Use Iface
123.234.123.0 * 255.255.255.0 U 0 0 0 eth0
192.168.0.0 * 255.255.0.0 U 0 0 0 vpn
default 123.234.123.1 0.0.0.0 UG 0 0 0 eth0
host# iptables -L -v
Chain INPUT (policy ACCEPT 1234 packets, 123K bytes)
pkts bytes target prot opt in out source destination
Chain FORWARD (policy ACCEPT 0 packets, 0 bytes)
pkts bytes target prot opt in out source destination
Chain OUTPUT (policy ACCEPT 2161K packets, 364M bytes)
pkts bytes target prot opt in out source destination
host# iptables -L -v -t nat
Chain PREROUTING (policy ACCEPT 0 packets, 0 bytes)
pkts bytes target prot opt in out source destination
Chain POSTROUTING (policy ACCEPT 0 packets, 0 bytes)
pkts bytes target prot opt in out source destination
Chain OUTPUT (policy ACCEPT 0 packets, 0 bytes)
pkts bytes target prot opt in out source destination
tinc 的配置
host# cat /etc/tinc/vpn/tinc.conf
Name = atwork
ConnectTo = home
host# cat /etc/tinc/vpn/tinc-up
#!/bin/sh
ifconfig $INTERFACE 192.168.10.20 netmask 255.255.0.0
host# ls /etc/tinc/vpn/hosts
atwork home
host# cat /etc/tinc/vpn/hosts/atwork
Address = 123.234.123.42
Subnet = 192.168.10.20/32
-----BEGIN RSA PUBLIC KEY-----
...
-----END RSA PUBLIC KEY-----
host# cat /etc/tinc/vpn/hosts/home
Address = 200.201.202.203
Subnet = 192.168.1.0/24
-----BEGIN RSA PUBLIC KEY-----
...
-----END RSA PUBLIC KEY-----
防火墻配置
firewall# ifconfig
ppp0 Link encap:Point-to-Point Protocol
inet addr:123.234.123.1 P-t-P:123.234.120.1 Mask:255.255.255.255
UP POINTOPOINT RUNNING NOARP MTU:1500 Metric:1
...
eth0 Link encap:Ethernet HWaddr 00:20:13:14:15:16
inet addr:123.234.123.1 Bcast:123.234.123.255 Mask:255.255.255.0
UP BROADCAST RUNNING MTU:1500 Metric:1
...
lo Link encap:Local Loopback
inet addr:127.0.0.1 Mask:255.0.0.0
UP LOOPBACK RUNNING MTU:3856 Metric:1
...
firewall# route
Kernel IP routing table
Destination Gateway Genmask Flags Metric Ref Use Iface
123.234.123.0 * 255.255.255.0 U 0 0 0 eth0
default 123.234.120.1 0.0.0.0 UG 0 0 0 ppp0
firewall# iptables -L -v
Chain INPUT (policy ACCEPT 1234 packets, 123K bytes)
pkts bytes target prot opt in out source destination
Chain FORWARD (policy DROP 1234 packets, 123K bytes)
pkts bytes target prot opt in out source destination
1234 123K ACCEPT tcp -- ppp0 eth0 anywhere 10.20.30.0/24 tcp flags:!SYN,RST,ACK/SYN
1234 123K ACCEPT any -- eth0 ppp0 10.20.30.0/24 anywhere
1234 123K ACCEPT tcp -- ppp0 eth0 anywhere 123.234.123.42 tcp dpt:655
1234 123K ACCEPT udp -- ppp0 eth0 anywhere 123.234.123.42 udp dpt:655
Chain OUTPUT (policy ACCEPT 2161K packets, 364M bytes)
pkts bytes target prot opt in out source destination
firewall# iptables -L -v -t nat
Chain PREROUTING (policy ACCEPT 0 packets, 0 bytes)
pkts bytes target prot opt in out source destination
Chain POSTROUTING (policy ACCEPT 0 packets, 0 bytes)
pkts bytes target prot opt in out source destination
Chain OUTPUT (policy ACCEPT 0 packets, 0 bytes)
pkts bytes target prot opt in out source destination
firewall # cat /etc/init.d/firewall
#!/bin/sh
echo 1 >/proc/sys/net/ipv4/ip_forward
iptables -P FORWARD DROP
iptables -F FORWARD
iptables -A FORWARD -j ACCEPT -i ppp0 -d 10.20.30.0/24 -p tcp ! --syn
iptables -A FORWARD -j ACCEPT -i eth0 -s 10.20.30.0/24
iptables -A FORWARD -j ACCEPT -i ppp0 -o eth0 -d 123.234.132.42 -p tcp --dport 655
iptables -A FORWARD -j ACCEPT -i ppp0 -o eth0 -d 123.234.132.42 -p udp --dport 655

 售前咨詢專員